The internet has transformed the way businesses, organisations, and individuals store information, communicate, and handle their daily activities. At the same time, the growing dependence on digital systems has also created new opportunities for cybercriminals to target vulnerable environments.
A weak website, unsecured network, exposed account, or outdated application can potentially provide an entry point for an attacker. This is where ethical hacking plays an important role.
Ethical hacking involves authorised security testing of computer systems, networks, applications, and digital assets to discover weaknesses before they can be misused by malicious attackers. Unlike illegal hacking, ethical hacking is carried out with the owner’s permission and within a clearly defined scope.
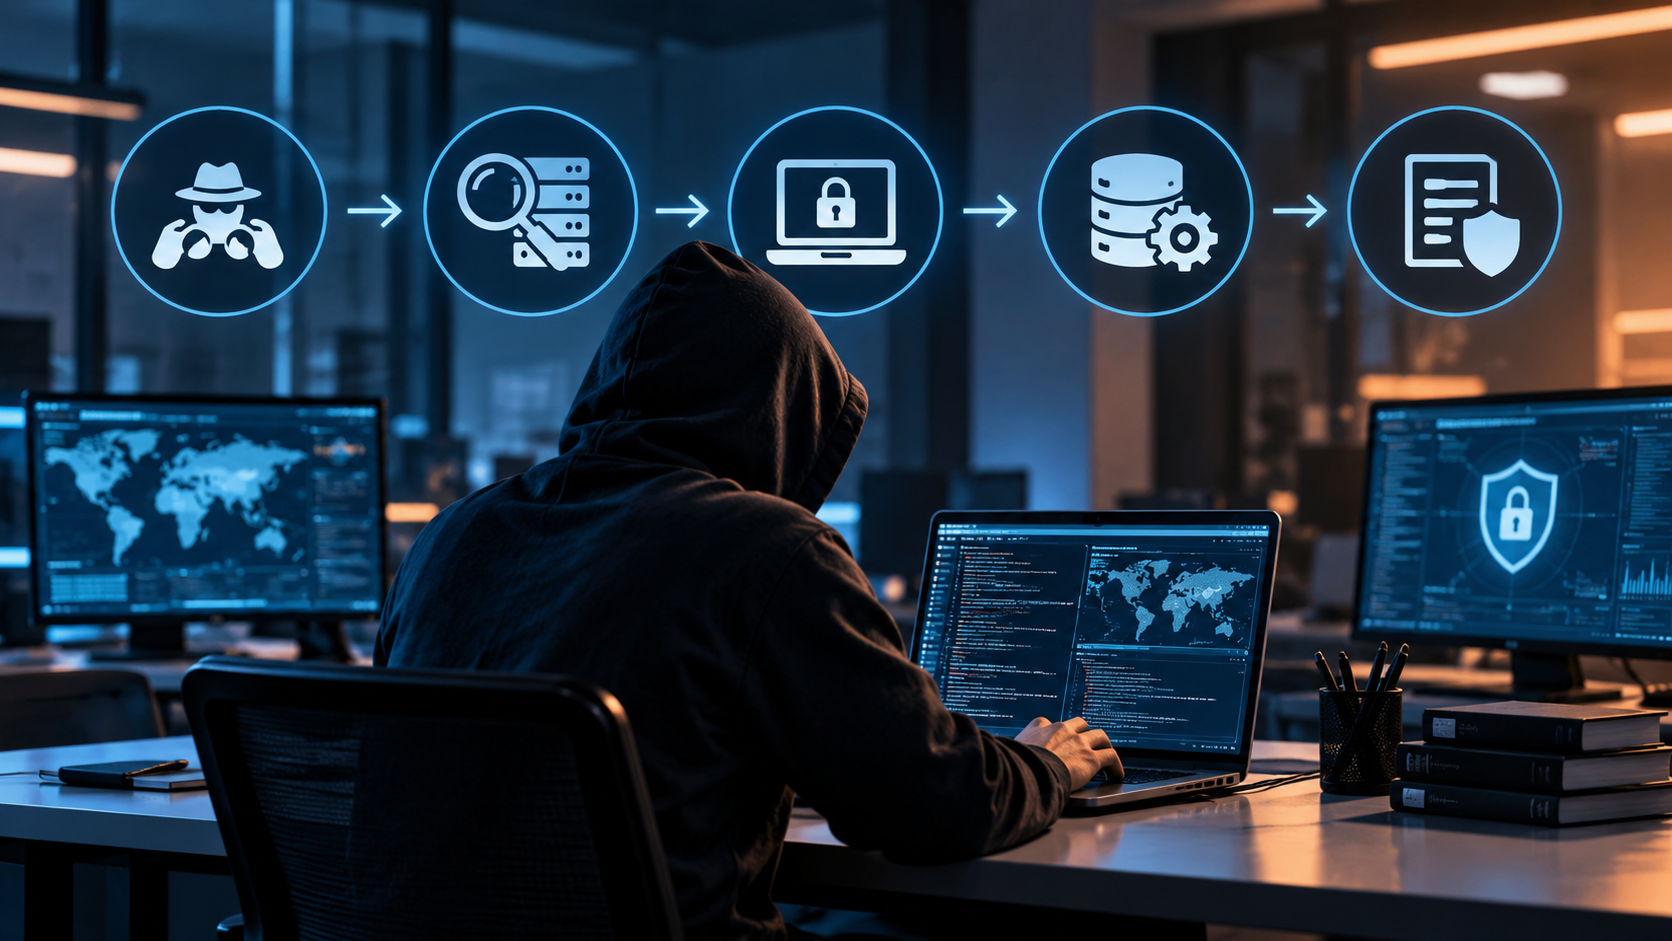
Professional security assessments generally follow a systematic process. Understanding these stages gives you a clearer picture of what an ethical hacker actually does while examining a system.
The five commonly discussed phases are reconnaissance, scanning, gaining access, maintaining access, and covering tracks. In legitimate security testing, the final phase is handled differently because the ethical hacker’s purpose isn’t to conceal criminal activity. Instead, the tester records relevant evidence, removes authorised testing artefacts when required, and reports the findings to the organisation.
Let’s look at each phase through a real-world example.
1. Reconnaissance: Gathering Information
The first phase is reconnaissance, sometimes called information gathering.
Before examining a system for weaknesses, an ethical hacker needs to build an understanding of the environment being tested. Imagine a security professional has been hired to assess a company’s website and network. The first step isn’t immediately trying to gain access. It involves learning about the organisation’s publicly visible digital presence.
The tester may examine information such as:
- Domain names
- Publicly available IP addresses
- Websites and subdomains
- Technologies used by a website
- Publicly exposed services
- Employee information available online
- Email formats
- Public documents and technical information
For example, suppose a company operates a main website along with several subdomains for different services. During reconnaissance, the security tester may identify these assets and check which ones are included in the authorised testing scope.
This stage is similar to examining a building before carrying out a security inspection. A tester needs to understand the available entrances, areas, and possible access points before evaluating how well they are protected.
The information collected during reconnaissance can provide direction for the later stages of a security assessment.
2. Scanning: Looking for Security Weaknesses
Once the available information has been collected, the next phase involves scanning and analysing the target environment.
The purpose is to understand how systems are configured and identify potential weaknesses that deserve further investigation.
Security professionals may examine:
- Open network ports
- Running services
- Operating systems
- Application versions
- Network configurations
- Security controls
- Potential vulnerabilities
For example, a scan might show that a server is operating a particular service or an older software version. This alone doesn’t prove that the system has been compromised. It simply identifies something that the ethical hacker may need to investigate more closely.
This distinction matters.
Automated vulnerability scanners can generate numerous alerts, but professional ethical hacking requires those results to be reviewed and validated instead of treating every alert as a confirmed security issue.
The tester may therefore combine automated tools with manual analysis to determine whether identified findings are genuine and relevant.
3. Gaining Access: Testing Whether a Vulnerability Can Be Exploited
This is the phase that most people associate with hacking.
After potential weaknesses have been identified, an authorised ethical hacker may conduct controlled exploitation to determine whether those vulnerabilities could actually provide unauthorised access.
The objective isn’t to damage the organisation or take sensitive information.
Instead, the tester is trying to establish questions such as:
Can this vulnerability actually be exploited?
What level of access could an attacker potentially obtain?
What information or systems could become exposed?
For example, imagine a web application has a weakness that could potentially allow one user to view information belonging to another user. During an authorised assessment, the ethical hacker may demonstrate the issue safely using test accounts and limited information.
This gives the organisation a clearer understanding of the actual risk instead of simply knowing that a vulnerability scanner has detected a possible problem.
It also helps security teams understand what could happen if a real attacker discovered the same weakness.
Ethical hackers must operate within clearly established rules during this phase. Testing systems or resources outside the agreed scope can create legal, operational, and security risks.
4. Maintaining Access: Understanding the Potential Impact
In a real cyberattack, gaining initial access may only be the beginning. Attackers can attempt to retain access to a compromised environment so they can return to it later.
During an authorised penetration test, security professionals may simulate relevant aspects of this behaviour to understand the possible consequences of a successful compromise.
The purpose is to evaluate how effectively an organisation can identify suspicious activity and respond to it.
For example, a security assessment may examine whether an attacker who gains control of one account could potentially reach additional systems or sensitive resources.
This can reveal weaknesses in areas such as:
- Access controls
- User privileges
- Network segmentation
- Account security
- Monitoring systems
- Incident detection
- Internal security policies
Consider a company where one employee account has limited permissions. If that account could potentially be used to reach sensitive internal systems, the organisation may have weaknesses in privilege management or network segmentation.
Ethical hacking can help uncover such weaknesses before they are discovered and exploited by an actual attacker.
5. Covering Tracks: What Ethical Hackers Actually Do
The fifth phase is traditionally described as covering tracks.
The term comes from malicious hacking scenarios in which attackers may attempt to remove or hide evidence of their activities after gaining access to a system.
Ethical hackers approach this area differently.
They don’t erase evidence to conceal illegal activity. During an authorised assessment, they may instead evaluate whether logging, monitoring, and security detection mechanisms are capable of identifying suspicious behaviour.
For example, a penetration tester may determine whether specific authorised testing activities produce alerts that a security team can detect and investigate.
The organisation can then assess whether its monitoring and incident response procedures are functioning effectively.
After the assessment, the ethical hacker documents the work carried out, removes authorised testing artefacts when necessary, and prepares a detailed report.
The report usually explains:
- What was tested
- Which vulnerabilities were identified
- How the vulnerabilities were validated
- Potential business impact
- Evidence supporting the findings
- Recommended remediation steps
This reporting stage is an important part of professional ethical hacking because identifying a vulnerability has limited value unless the organisation understands the problem and knows what actions can be taken to address it.
Why Understanding These Phases Matters
Ethical hacking isn’t simply about running hacking tools or trying random passwords.
It follows a planned security testing methodology.
A professional ethical hacker needs to understand the target, identify possible weaknesses, verify vulnerabilities safely, determine their potential impact, and communicate the findings clearly.
This requires knowledge of several areas, including:
- Networking
- Linux
- Windows security
- Web application security
- Vulnerability assessment
- Penetration testing
- Cryptography
- Authentication and access control
- Security monitoring
- Cybersecurity principles
This is why practical learning is important for anyone considering a career in cybersecurity.
Ethical Hacking Training
People interested in cybersecurity often explore Ethical Hacking to understand how security testing works in real-world environments.
Ethical Hacking training generally focuses on identifying vulnerabilities, learning penetration testing methodologies, using security testing tools, and understanding controlled attack simulations.
Students can also learn how security weaknesses may affect websites, networks, applications, and other digital systems. This practical understanding helps learners see how attackers identify weaknesses and how security professionals test and strengthen those areas.
For beginners, practical exercises can make these concepts easier to understand. Instead of studying only theoretical definitions, students can explore how reconnaissance is performed, how vulnerabilities are assessed, how security controls are tested, and how security findings are documented.
Building a Career in Ethical Hacking
Ethical hacking offers several career opportunities for learners who are interested in testing and protecting digital systems.
Depending on their skills and interests, learners can explore roles such as:
- Ethical Hacker
- Penetration Tester
- Vulnerability Assessment Analyst
- Security Operations Centre Analyst
- Network Security Specialist
- Application Security Tester
- Information Security Analyst
- Security Testing Specialist
Developing a strong technical foundation can help learners understand these different roles and identify the area that matches their interests.
For students and beginners, structured Ethical Hacking training can provide a starting point for developing practical knowledge, security testing skills, and an understanding of common vulnerabilities.
Learn Ethical Hacking with Skill Haara
Skill Haara provides training opportunities for learners interested in developing practical skills in ethical hacking.
The institute has centres in Trivandrum, Thrissur, and Aluva, giving students from different parts of Kerala access to ethical hacking-focused learning.
Those specifically looking for Ethical Hacking training can explore the Diploma in Cyber Security and Ethical Hacking program offered by Skill Haara.
Students can learn about different areas of security testing and gain an understanding of how ethical hackers identify, assess, and report vulnerabilities in authorised environments.
Final Thoughts
The five phases of ethical hacking demonstrate that security testing involves much more than simply attempting to enter a computer system.
The process starts with understanding the target, moves through vulnerability identification and validation, examines what could happen after a successful compromise, and finishes with proper documentation and recommendations for addressing security issues.